

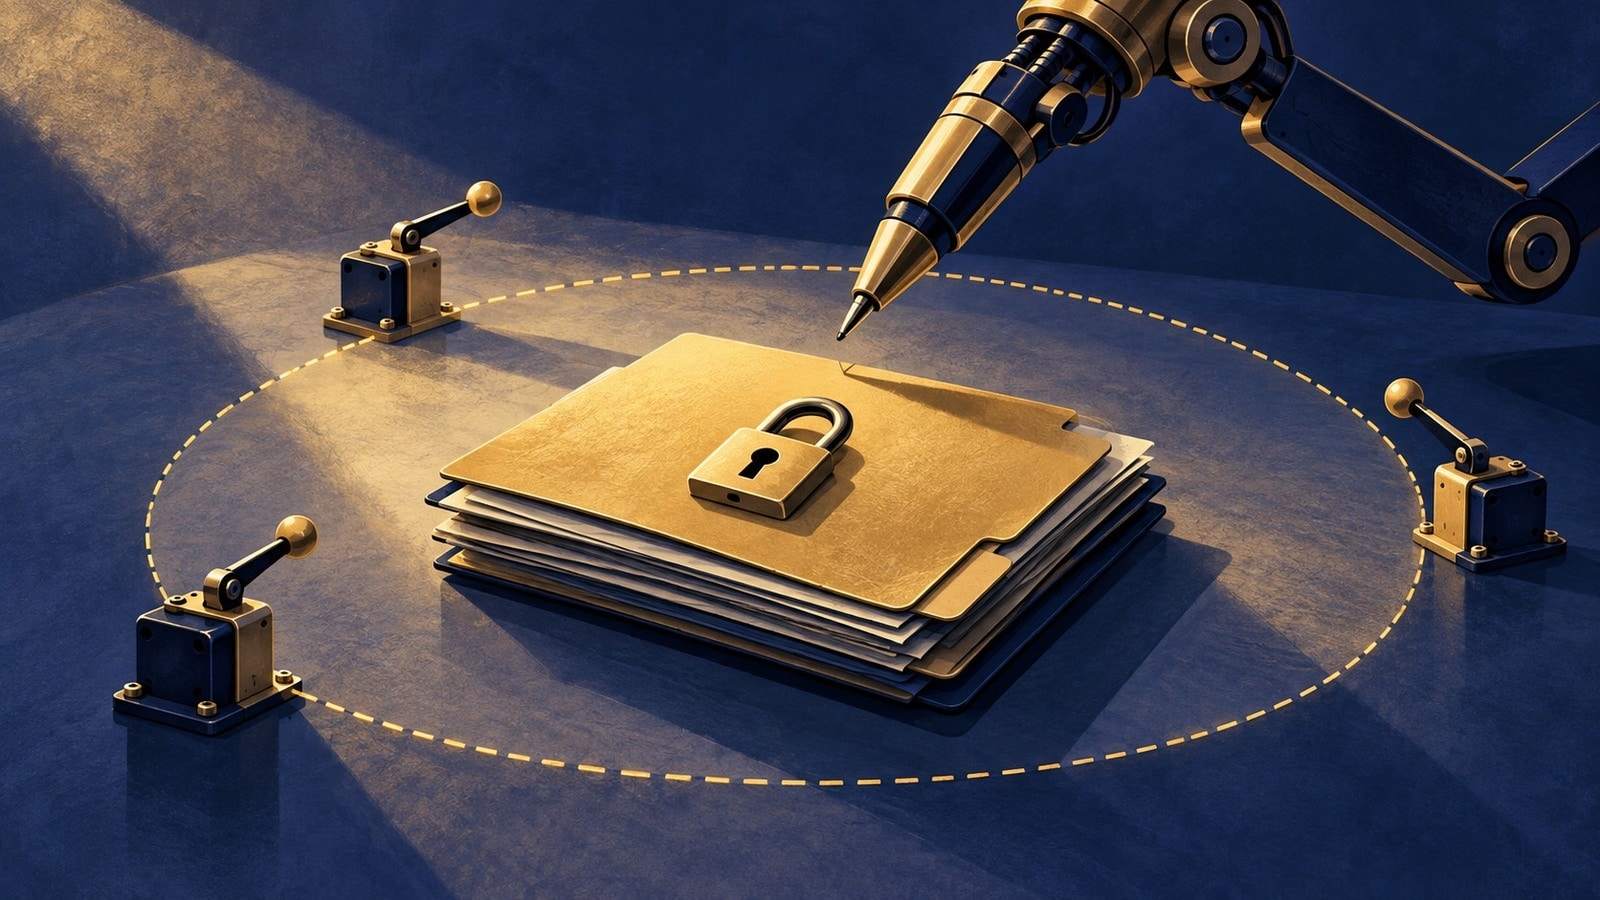
A demonstration becomes an agent when its words acquire access to things that matter. The assistant can move from suggesting a change to making it, from drafting a message to sending it, from reading a record to altering the record. That transition is often presented as a product upgrade. It is also a transfer of authority. The most important design question is who can end that transfer, and how quickly the system obeys.
False Normal supplies the anchor through an AI operating under explicit restrictions and a reversible, logged grant of access. This article does not use the novel as evidence that its AI mechanisms are real. It uses the permission boundary as a way to inspect real agents. Cyberdelia's angle is administrative power: an intelligent explanation of why an action would be helpful should not become the credential that authorizes the action.
There are at least three separate questions. Can the model produce a request? Can a tool execute that request? Is the requested operation allowed for this user in this context? Conflating them makes the system difficult to govern. A model may be excellent at planning while having no legitimate authority over a particular account. A tool may accept well-formed input while lacking the context needed to decide whether the operation is permitted. Authorization has to remain a property of the surrounding system.
OWASP's guidance on excessive agency describes risks arising from too much functionality, permission, or autonomy. Its recommendations include limiting available tools and enforcing authorization in downstream systems. That separation is valuable because model behavior is not a dependable access-control boundary. An instruction to be careful can be part of the user experience. It cannot replace a service that rejects operations outside the user's actual permissions.
Consider a hypothetical assistant that helps an office reconcile expenses. Reading a designated folder and drafting a discrepancy report may be appropriate. Access to the entire organization's storage and payment system is a different grant. Product teams sometimes attach broad credentials because narrow integration takes more work. The resulting assistant can then do much more than its task requires, and every misunderstood instruction or hostile document has a larger field in which to cause trouble.
A scoped grant would identify the resource, permitted operations, purpose, and duration. The assistant might read this month's receipts and write a draft in one review folder for the next hour. It would not acquire a permanent identity with every permission held by the person who connected it. This is a proposed architecture, and implementations will vary. The aim is to make authority describable in terms a human can inspect before the system acts.
Expiration is useful because projects end, people change roles, and temporary needs are easily forgotten. A time limit makes continued access a fresh decision. It also creates engineering requirements. The service must check validity when an operation occurs, not only when a session begins. A cached credential that remains usable after the grant expires defeats the visible promise. Long-running jobs need a defined rule for what happens when their authority runs out halfway through the task.
Revocation needs similar precision. Disabling a button in the interface is not enough if queued operations, background workers, or delegated tokens continue to act. A credible revocation path identifies those components and prevents new effects as soon as the policy allows. Some actions may already be irreversible. The system should expose that fact rather than imply that revoke rewinds history. Ending authority and undoing an action are separate capabilities.
Approval screens can fail even when the underlying policy is sound. A user cannot review a consequential operation from a vague sentence such as finish the task. The request should identify the concrete change, affected resources, and material consequences. When several operations are bundled, the grouping should correspond to a decision the user can actually assess. Repetitive low-information prompts train people to approve mechanically, making the interface noisy without making authority more deliberate.
The model should not write its own final authorization policy. It can explain why it wants access, propose a narrower scope, and identify missing permissions. Another component must evaluate the request against established rules. Otherwise the agent becomes both applicant and approver. This distinction is especially important when the agent reads untrusted material. A persuasive passage in a document should not be able to enlarge the tool set available to the process reading that document.
Logging should make the delegation legible afterward. Useful records include the grant, its issuer, the scope, the tool request, the policy decision, and the resulting change. Recording the model's prose alone is inadequate because prose can misdescribe what a tool actually did. A review should be able to distinguish a proposed operation, an authorized attempt, a failed execution, and a completed effect. Each answers a different question when somebody asks why a record changed.
Reversibility is an additional design goal, not an excuse for unlimited permissions. Writing to a draft, staging a change, and keeping a version history can create room for review. But rollback has limits. A disclosed secret cannot be undisclosed. A sent message cannot reliably be removed from every recipient's possession. A deletion may have consequences before recovery occurs. Task planning should favor reversible steps where possible while treating irreversible steps as distinct decisions.
Evaluation should test refusal and shutdown as seriously as task completion. Can the agent complete the permitted task with a narrow grant? Does it stop when access expires? Can hostile input convince it to attempt an operation outside the scope, and does the tool reject that attempt? Does the user see an accurate account of failure? These tests reveal whether the system's advertised boundaries exist in operation or only in documentation.
An agent worth trusting is not one that always finds a reason to continue. It is one whose useful authority can be specified, inspected, limited, and ended. Capability makes the permission slip more important. The slip should name the job, identify the issuer, and expire when the job no longer justifies the access.
An agent's intelligence does not authorize its actions. Useful delegation needs scoped grants, downstream enforcement, expiry and a revocation path that actually stops work.
Nine technologies behind False Normal
Independent technical essays inspired by manuscript concepts. No plot recap or ending reveals.
- The Implant Outlives the Company. Who Keeps the Body Working?
- A Scanner Finds a Match. The Institution Invents the Rest.
- The Person Watching Your Vitals Should Not Automatically Own Your Day
- When Your Eyes Come With a Ranking System
- A Perfect Hash Can Preserve a Perfect Lie
- The Air Gap Ends Where the File Begins
- An AI's Permission Slip Should Expire
- Two Timestamps Are Not Yet a Sequence of Events
- A Digital Tripwire Tells You Something Touched It. Now What?