
CLAIM CHECK / ECONOMICS OF CYBERCRIME
Cybercrime has always had a labor problem. Finding a target is cheap; turning scattered clues into a working route through a real organization takes time, attention, and a willingness to repeat dull work. Artificial intelligence does not erase those constraints. It can make some of the dull work cheaper, easier to delegate, and easier to run against more targets at once.
That is the economic question behind the South Korean financial-sector intrusions now being described as AI-assisted. The story is not that a machine woke up, chose a bank, and autonomously defeated a national banking system. The public record points to a human operator using an agentic penetration-testing tool and large language models during a campaign that touched financial organizations. Those are serious findings. They are also narrower than the most dramatic summaries suggest.
As of November 2, 2026, South Korea’s Financial Services Commission (FSC) has confirmed a widening set of data-breach incidents across financial firms. The agency has not publicly concluded that one AI system caused all of them. The technical evidence for ARTEX and LLM use comes from investigators examining attacker-controlled infrastructure and from Korean reporting that quotes the Financial Security Institute (FSI). The causal link between that toolchain and each victim incident remains a separate question.
Two timelines, two kinds of evidence
The first timeline is the victim record. On October 14, the FSC said 16 companies across the financial sector had experienced recent data-breach incidents, with roughly 100,000 pieces of customer data estimated to be affected. The commission said passwords and credit-card numbers had not been reported among the exposed data. It also said the Financial Supervisory Service and FSI were still examining attack paths, whether incidents were linked, whether they came from the same attacker, and whether AI had been used.
That official count is the safest scale figure to repeat, with its date attached. It does not mean that 16 institutions were all breached by one person, with one tool, through one chain. It does not establish that every incident involved AI. The government described a set of confirmed incidents and an investigation into relationships among them.
The second timeline is the attacker-tool evidence. On October 2, South Korean reporting described ARTEX strings appearing on infrastructure associated with attacks, while noting that use of the tool in the Shinhan Bank incident had not yet been confirmed. The next day, Herald Business reported in Korean that an FSI official said investigators traced attack IP addresses and Shinhan logs and found indications ARTEX had been used. The same report made a distinction that later headlines sometimes blur: a human hacker used the AI tool; the tool had not independently attacked the bank.
On October 7, CrowdStrike published a technical analysis of infrastructure it associated with the campaign. Researchers said open directories on attacker-controlled servers contained Claude Code session histories, ARTEX configuration files, and Claude memory files. They described a two-server setup and activity from late September into early October. Their post said the number of affected organizations was unconfirmed and did not attribute the activity to a named group. Its assessment that the operator was likely Chinese-speaking and financially motivated was explicitly a moderate-confidence judgment, not a verified identity.
On November 1, The Washington Post reported a more specific alleged operator profile, drawing on CrowdStrike’s investigation and digital traces. That is a new journalistic account of the investigation, not a new public finding by South Korean authorities. The identity, age, location, and actions attributed to an individual remain allegations reported from that investigation. Cyberdelia has not independently verified the person behind the activity, and the identity is not needed to assess the technical lesson.
What the toolchain can change
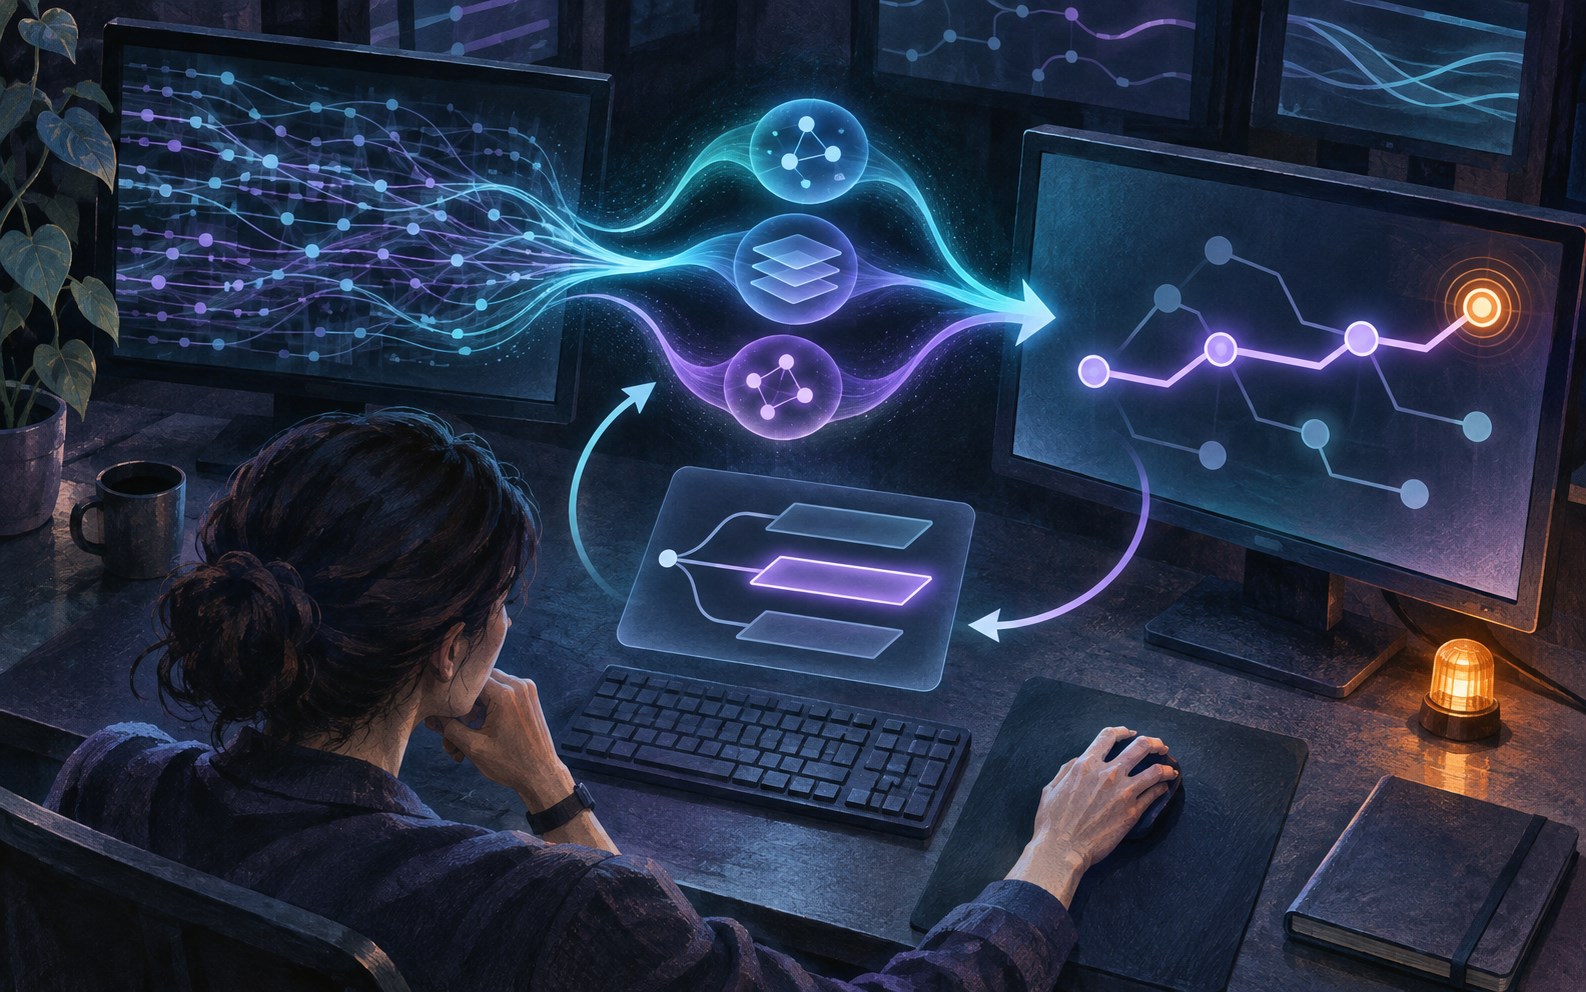
ARTEX is described by CrowdStrike and Korean reporting as an open-source, agentic penetration-testing system. In an authorized assessment, software of this kind can help a tester enumerate a system, inspect results, choose a next test, and coordinate security tools. In unauthorized hands, the same loop can be redirected. A large language model can turn output into a concise next-step suggestion, translate between tools, draft or adapt code, and keep a task moving through steps that would otherwise demand a human operator’s attention.
The key economic effect is not magic access. It is a change in the amount of human effort needed to explore each target and interpret each result. If a process that once required an experienced operator to inspect every response can be partly scripted, summarized, or run in parallel, the operator’s time stretches farther. A less experienced person may also be able to use a workflow that previously required more specialist knowledge. The likely advantage is throughput and lower friction, not a guarantee of deeper skill.
That is why “AI-powered” can mislead when it is used as a single explanation. There are at least four different claims hiding inside the phrase:
- Tool use: an operator used an AI model or agent during the operation.
- Task assistance: the model helped with reconnaissance, code, interpretation, or planning.
- Material contribution: that assistance made a meaningful difference to access, scale, or impact.
- Autonomy: the system selected and carried out the operation without meaningful human direction.
The available reporting supports the first claim and gives credible evidence for the second. The third is plausible but has not been measured publicly against a no-AI counterfactual. The fourth is not supported: the Korean report quoting the FSI explicitly described human use of the tool, and the exposed session files CrowdStrike analyzed show an operator’s working environment, not a machine acting outside human control.
Traditional automation already scans ports, tests known weaknesses, and runs exploit chains. AI does not deserve credit for every task that can be automated. Its added value is often the glue around existing tools: changing formats, summarizing noisy output, generating a plausible next action, or assisting an operator who does not know every command by memory. Those are useful advantages in a long campaign because small reductions in effort compound across many targets.
The weak link may be beside the vault
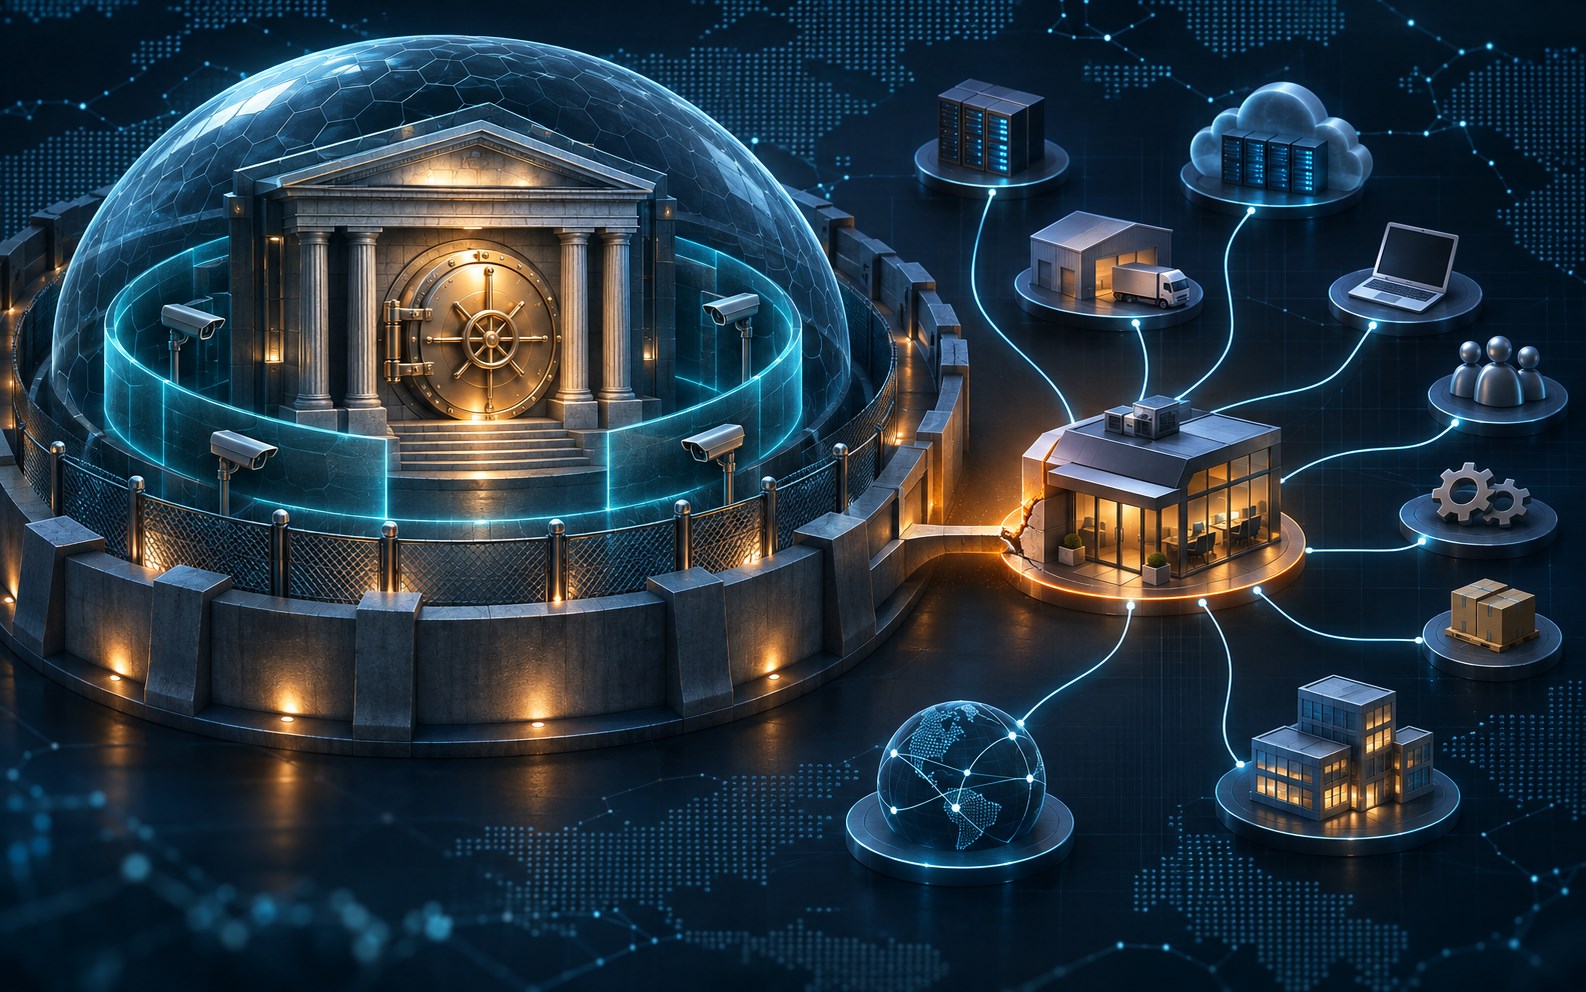
Public accounts of the Korean incidents describe targets such as broker-facing loan inquiry services and employee mobile work-support systems. CrowdStrike presented those details as industry reporting, not as a full victim-system forensic record released for independent review. They should not be generalized to all 16 firms. Still, they point to a familiar security pattern: the core payment system can be tightly controlled while the surrounding services that feed employees, brokers, contractors, and customers receive less attention.
This is the part of the story that does not need an AI explanation. A support portal can expose sensitive data because its access checks, session handling, software maintenance, or vendor boundaries are inadequate. An attacker can exploit that weakness with a browser, a script, or a commercial scanner. AI assistance may make it faster to find and test the weakness. It does not create the weak configuration, and it does not explain why the system was reachable in the first place.
The economic effect matters because attackers can test more doors per hour. It does not change the defender’s basic obligation to know which doors exist. Security teams need a current inventory of public services and their owners, including broker portals, mobile workforce tools, staging systems, forgotten APIs, and third-party support products. If a service handles sensitive information, it belongs in the organization’s threat model even when it is not part of the ledger or payment core.
Access controls should assume that a public-facing support tool will eventually be probed. Strong authentication, short-lived sessions, least privilege, rate limits, monitoring for unusual export volume, and isolation between support functions and core records reduce the value of a foothold. Vendor connections should be reviewed as production access paths, not treated as paperwork at the edge of the network.
The economics are measurable—if defenders measure them
“AI made the attack cheaper” is a reasonable hypothesis, but the public sources do not provide an hourly cost, a model-by-model comparison, a baseline for the operator’s prior skill, or a controlled estimate of how much faster the campaign ran. Nobody should manufacture those numbers from a dramatic headline.
Organizations can measure the defensive version of the same question. Give a red team permission to test a defined external surface with both conventional tooling and approved AI assistance. Record how long it takes to discover assets, validate a finding, reach sensitive data, and produce a reproducible report. Then measure how quickly the blue team detects the activity, blocks the path, and fixes the underlying flaw. Repeat the exercise after changes. The useful metric is not whether somebody used a chatbot; it is whether the organization’s controls still work when an operator can iterate faster.
AI also gives defenders a way to triage more telemetry, summarize incident timelines, compare configurations, and prioritize exposed services. That can help a small team cover more ground. It can also create a second automation problem: analysts may accept a plausible summary without checking the raw event, or let an agent take actions that should require a human. Defensive AI needs clear permissions, audit trails, and a stop button that works before an automated response locks out the wrong system.
What is established—and what is still open
Evidence ledger
- KNOWN: The FSC reported 16 financial companies with recent data-breach incidents by October 14 and estimated roughly 100,000 affected data items. This is a regulator’s dated count, not a count of AI-caused attacks.
- REPORTED: The Herald Business’ October 3 Korean report quoted an FSI official describing ARTEX traces in logs and IP investigations tied to the first-reported Shinhan case. CrowdStrike separately described ARTEX files and LLM session histories on infrastructure it associated with the activity.
- INFERRED: Agentic tooling can lower the operator time needed for repeated reconnaissance and interpretation. That mechanism is credible; its contribution to this campaign has not been quantified publicly.
- HYPOTHESIZED: AI assistance materially increased the number of financial targets the operator could test or the speed at which data could be reached.
- UNKNOWN: A definitive public attribution; a victim-by-victim account of AI use; an independently released forensic chain from affected systems; the measured time or cost reduction; and whether every institution in the regulator’s 16-company count was connected to one campaign.
Cyberdelia assessment
The strongest conclusion is narrower than “AI hacked South Korea’s banks,” and more useful. South Korea confirmed a broad set of financial-sector breach incidents. Korean reporting attributed ARTEX traces in the Shinhan investigation to the FSI. CrowdStrike’s analysis found artifacts consistent with ARTEX and LLM use on attacker-controlled infrastructure and linked that environment to activity against South Korean financial organizations. The Washington Post’s November 1 report adds an alleged operator profile based on that investigation. The evidence supports AI-assisted work in the campaign; it does not prove that AI autonomously breached every institution or that AI alone explains the scale.
The economic shift is still real enough to prepare for. A criminal does not need to become an exceptional exploit developer if tools can help assemble reconnaissance, testing, and interpretation into a repeatable workflow. The advantage is measured in lower friction and more attempts, not in a machine’s independent intent. For defenders, the answer is to shrink the number of weak routes and shorten the time between exposure, detection, and repair.
That work was already overdue. AI changes the price of looking for the unlocked side door. It does not make the side door disappear.
Sources and method
This feature is a claim check and mechanism analysis. We compared South Korean regulator statements, original Korean reporting, a first-party technical investigation, and the November 1 follow-up report. We did not inspect victim systems, reproduce the intrusion, independently identify the alleged operator, or estimate an attacker’s costs.
- Financial Services Commission, “Authorities Hold Meeting on Cybersecurity Management in Financial Sector to Bolster Anti-Hacking Measures,” October 14, 2026. Primary regulator source for the 16-company estimate and the ongoing investigation into links and AI use.
- Herald Business, “[단독] 은행 연쇄 해킹 도구는 중국 ‘아르텍스 AI’…해커가 사용했다,” October 3, 2026 (Korean original). Original reporting that quotes an FSI official on ARTEX traces in Shinhan logs/IP work and distinguishes human use from an autonomous attack. English edition.
- CrowdStrike Intelligence, “Unknown Threat Actor Uses AI-Driven ARTEX to Target South Korean Finance,” October 7, 2026. First-party technical analysis of attacker-controlled infrastructure, ARTEX configuration, and Claude Code session material; the company states that the number of affected organizations was unconfirmed and gives its attribution assessment with confidence limits.
- The Washington Post, “A wave of new cyberattacks is just getting started,” November 1, 2026. Follow-up reporting on CrowdStrike’s alleged operator and the broader cybercrime implications.
- Newsis, “AI 해킹 먹잇감 된 은행권…금융당국도 보안 대응 ‘비상’,” October 2, 2026 (Korean). Early reporting that distinguished observed ARTEX-related strings from confirmation that the tool was used in a specific bank incident.
Corrections and material updates: Cyberdelia Corrections. If new regulator or forensic evidence changes the status of a claim, this page will be updated with the dated change.
This feature will be updated if the FSC, FSS, FSI, police, affected institutions, or independently reviewable technical evidence materially changes these findings. Updates will be dated here.